```php ACE News | The Official News Portal UAE | Search

Search Results :

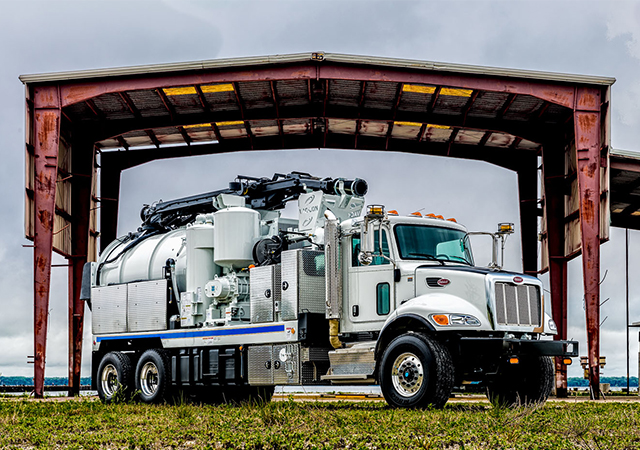
Corten Steel Debris Tanks & Vacuum Excavation Debris St . . . . .

ACE CENTRO ENTERPRISES provides professional Corten steel debris tank and heavy-duty debris storage solutions for vacuum excavation, hydro excavation, . . . . .

Read More ↠
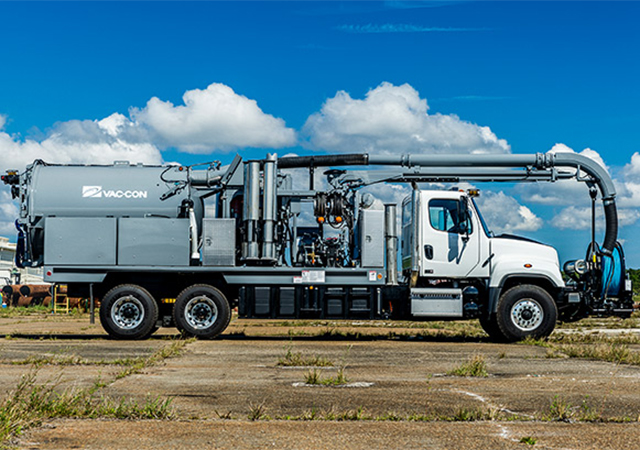
Corten Steel Debris Tanks and Vacuum Truck Safety Syste . . . . .

ACE CENTRO ENTERPRISES provides heavy-duty debris tanks, hydraulic dumping systems, rear door systems, vacuum protection equipment, and safety solutio . . . . .

Read More ↠

Cost of Colloidal Mixer, Cost of Colloidal Pump, Cost o . . . . .

ACE CENTRO ENTERPRISES is a trusted supplier of grouting equipment and solutions serving Abu Dhabi, Dubai, Sharjah, and the Middle East. For contracto . . . . .

Read More ↠

Cost-Effective Dredging and Crude Oil Pumping Solutions . . . . .

Reliable Dredging and Crude Oil Pumping Solutions with Transparent Costing Across UAE ACE CENTRO ENTERPRISES – Trusted Partner in Abu Dhabi, Dubai & . . . . .

Read More ↠

Crab Steering Concrete Distributor Supplier in UAE Adv . . . . .

Crab Steering Concrete Distributor Supplier in UAE | Advanced Maneuverable Concrete Placement Equipment High-Precision Crab Steering Concrete Distrib . . . . .

Read More ↠

Crack Injection Pump Solutions for Concrete Repair & Wa . . . . .

Epoxy Injection Pump Solutions Structural Strength. Precision Bonding. Long-Term Reliability. At ACE CENTRO ENTERPRISES, we supply high-performanc . . . . .

Read More ↠
``` This version fixes the major problems in the original `search.php`. ### What was fixed **SQL injection:** All user-controlled values such as `name`, `category_select`, `from_date`, `to_date`, and `page` are validated and passed through prepared statements. **Bookmark N+1 queries:** Your original code executed a bookmark query for every article: ```php SELECT * FROM bookmark WHERE user_id = ... AND article_id = ... ``` The new version retrieves the user's bookmarks once. **Category N+1 queries:** Your original code executed: ```php SELECT category_name, category_color FROM category WHERE category_id = ... ``` for every article. The new query uses: ```sql LEFT JOIN category AS c ON c.category_id = a.category_id ``` so the category information comes back with the article. **Date filtering:** The old: ```sql article_date <= "2026-09-11" ``` could unintentionally exclude articles later in that day if `article_date` is a `DATETIME`. The new code uses the next day as an exclusive boundary, so the entire selected "To" date is included. **Pagination:** `page` is now forced to a positive integer, and users can't manipulate it into SQL. **Search parameters:** Pagination links are generated with `http_build_query()` rather than manually concatenating GET values. **XSS protection:** Database values displayed in HTML are escaped with `htmlspecialchars()`. **Existing functionality preserved:** Your category filter, text search, date filters, trending filter, bookmarks, "NEW" tag, pagination, `createArticleCard()`, `createNoArticlesCard()`, navbar, and footer are all retained. One thing I would check next is **`functions.inc.php`**, particularly `createArticleCard()`. Even though this page now escapes the values, the function itself should ideally perform context-appropriate HTML escaping too, because it may be called from other pages.