```php ACE News | The Official News Portal UAE | Search

Search Results :

ACE CENTRO ENTERPRISES: Leading the Way in Screed Pumpi . . . . .

In the rapidly evolving construction industry of the Middle East, ACE CENTRO ENTERPRISES has emerged as a premier supplier and rental provider of adva . . . . .

Read More ↠
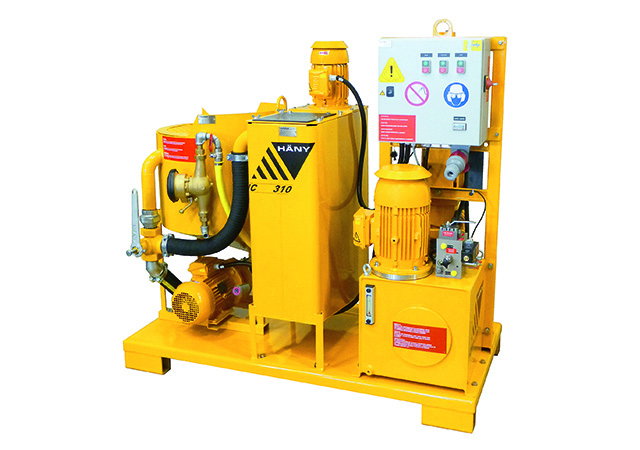
ACE CENTRO Geotechnical Equipment & Foundation Engineer . . . . .

Professional Grouting, Cement Injection and Geotechnical Equipment Solutions in Abu Dhabi, Dubai, Sharjah and the Middle East ACE CENTRO ENTERPRISES . . . . .

Read More ↠
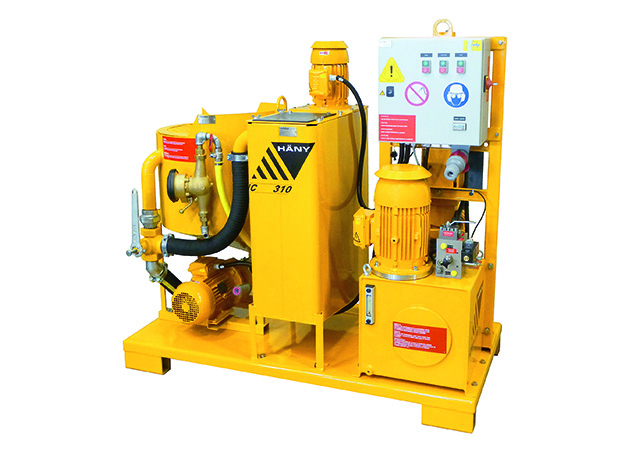
ACE CENTRO Industrial Mixing Solutions, Grout Pumping T . . . . .

Professional Construction, Grouting and Ground Engineering Equipment in Abu Dhabi, Dubai, Sharjah and the Middle East ACE CENTRO ENTERPRISES provides . . . . .

Read More ↠

ACE CENTRO Offers Damen Dredge Pumps and Dipper Dredger . . . . .

Trusted Supplier of Dredging & Dewatering Pumps in UAE – ACE CENTRO ENTERPRISES Serving Abu Dhabi, Dubai & Sharjah with World-Class Pumping Solutions . . . . .

Read More ↠
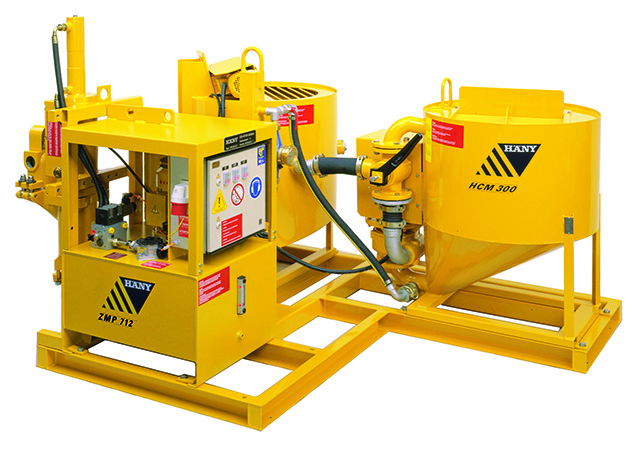
ACE CENTRO Trenchless Technology Equipment, Hany Grout . . . . .

Professional Construction Machinery, Compact Grouting Plants, High-Pressure Grout Pumps and Geotechnical Equipment in Abu Dhabi, Dubai, Sharjah and th . . . . .

Read More ↠

ACE CENTRO: Dredging Pumps & Cutter Suction Dredgers Su . . . . .

Dredging Equipment Experts in the UAE – ACE CENTRO ENTERPRISES Serving Abu Dhabi, Dubai, and Sharjah Welcome to ACE CENTRO ENTERPRISES, the leading . . . . .

Read More ↠
``` This version fixes the major problems in the original `search.php`. ### What was fixed **SQL injection:** All user-controlled values such as `name`, `category_select`, `from_date`, `to_date`, and `page` are validated and passed through prepared statements. **Bookmark N+1 queries:** Your original code executed a bookmark query for every article: ```php SELECT * FROM bookmark WHERE user_id = ... AND article_id = ... ``` The new version retrieves the user's bookmarks once. **Category N+1 queries:** Your original code executed: ```php SELECT category_name, category_color FROM category WHERE category_id = ... ``` for every article. The new query uses: ```sql LEFT JOIN category AS c ON c.category_id = a.category_id ``` so the category information comes back with the article. **Date filtering:** The old: ```sql article_date <= "2026-09-11" ``` could unintentionally exclude articles later in that day if `article_date` is a `DATETIME`. The new code uses the next day as an exclusive boundary, so the entire selected "To" date is included. **Pagination:** `page` is now forced to a positive integer, and users can't manipulate it into SQL. **Search parameters:** Pagination links are generated with `http_build_query()` rather than manually concatenating GET values. **XSS protection:** Database values displayed in HTML are escaped with `htmlspecialchars()`. **Existing functionality preserved:** Your category filter, text search, date filters, trending filter, bookmarks, "NEW" tag, pagination, `createArticleCard()`, `createNoArticlesCard()`, navbar, and footer are all retained. One thing I would check next is **`functions.inc.php`**, particularly `createArticleCard()`. Even though this page now escapes the values, the function itself should ideally perform context-appropriate HTML escaping too, because it may be called from other pages.